Close the public management door.
Supported agents connect outbound. You do not normally need public inbound SSH, RDP or other management ports for these paths.
Find the server that needs attention. Investigate through a secure terminal or remote desktop, then review its monitoring and recovery information. All in Central.
From £10/monthUp to 5 devices · Ex VATView plans ↗
ONE INVESTIGATION. ONE PLACE.
A CPU finding. A device workspace. The tools to investigate. Follow one example through Central in this short, silent product tour.
 Central / Infrastructure viewDEMO ENVIRONMENT
Find the issue
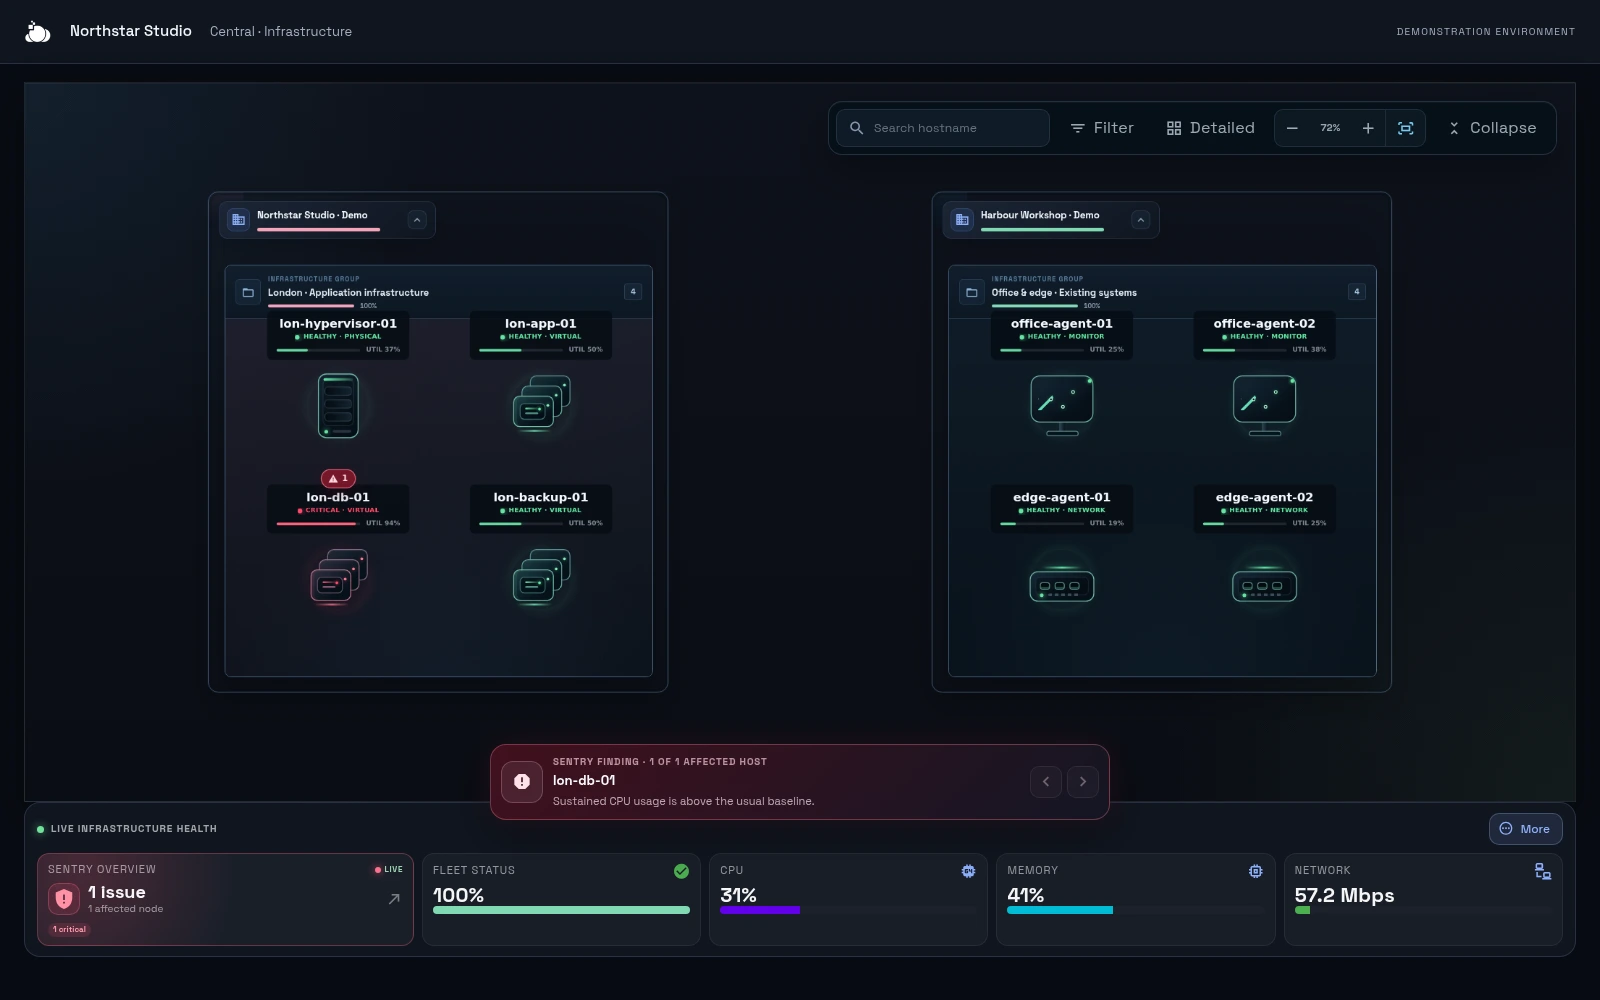
Central flags unusual CPU usage on lon-db-01. Start with the affected device, in the context of your estate.
Infrastructure view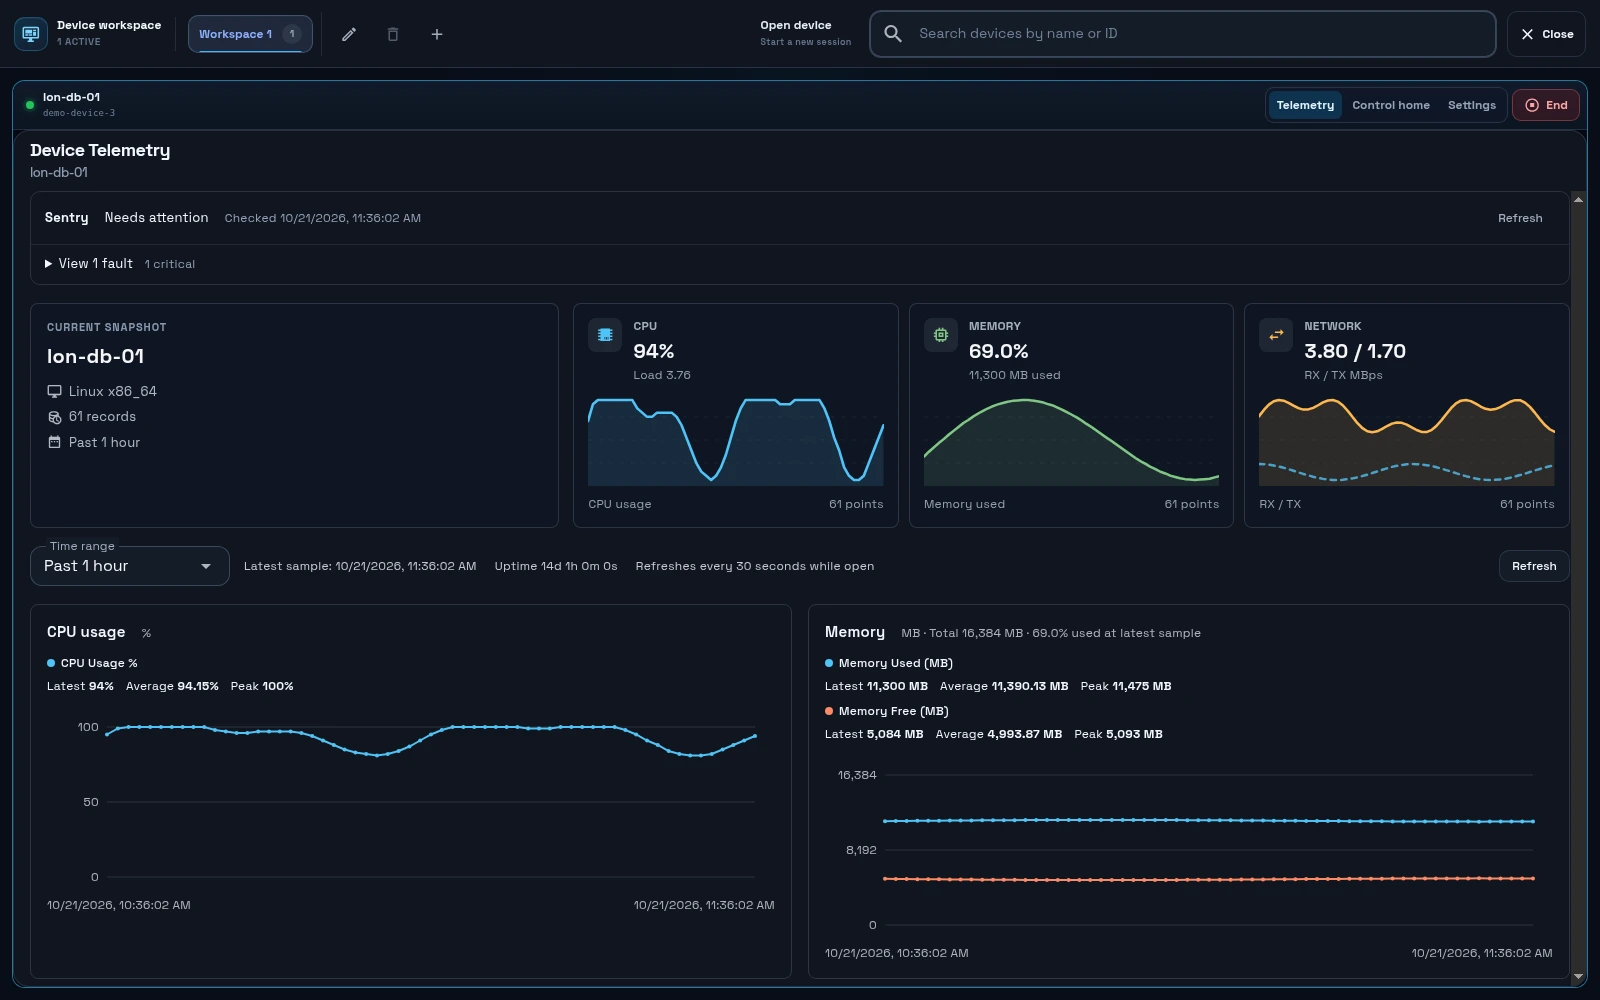
Inspect the device
Open the device’s telemetry. Review the CPU trend, memory and network activity before choosing your next step.
Device telemetry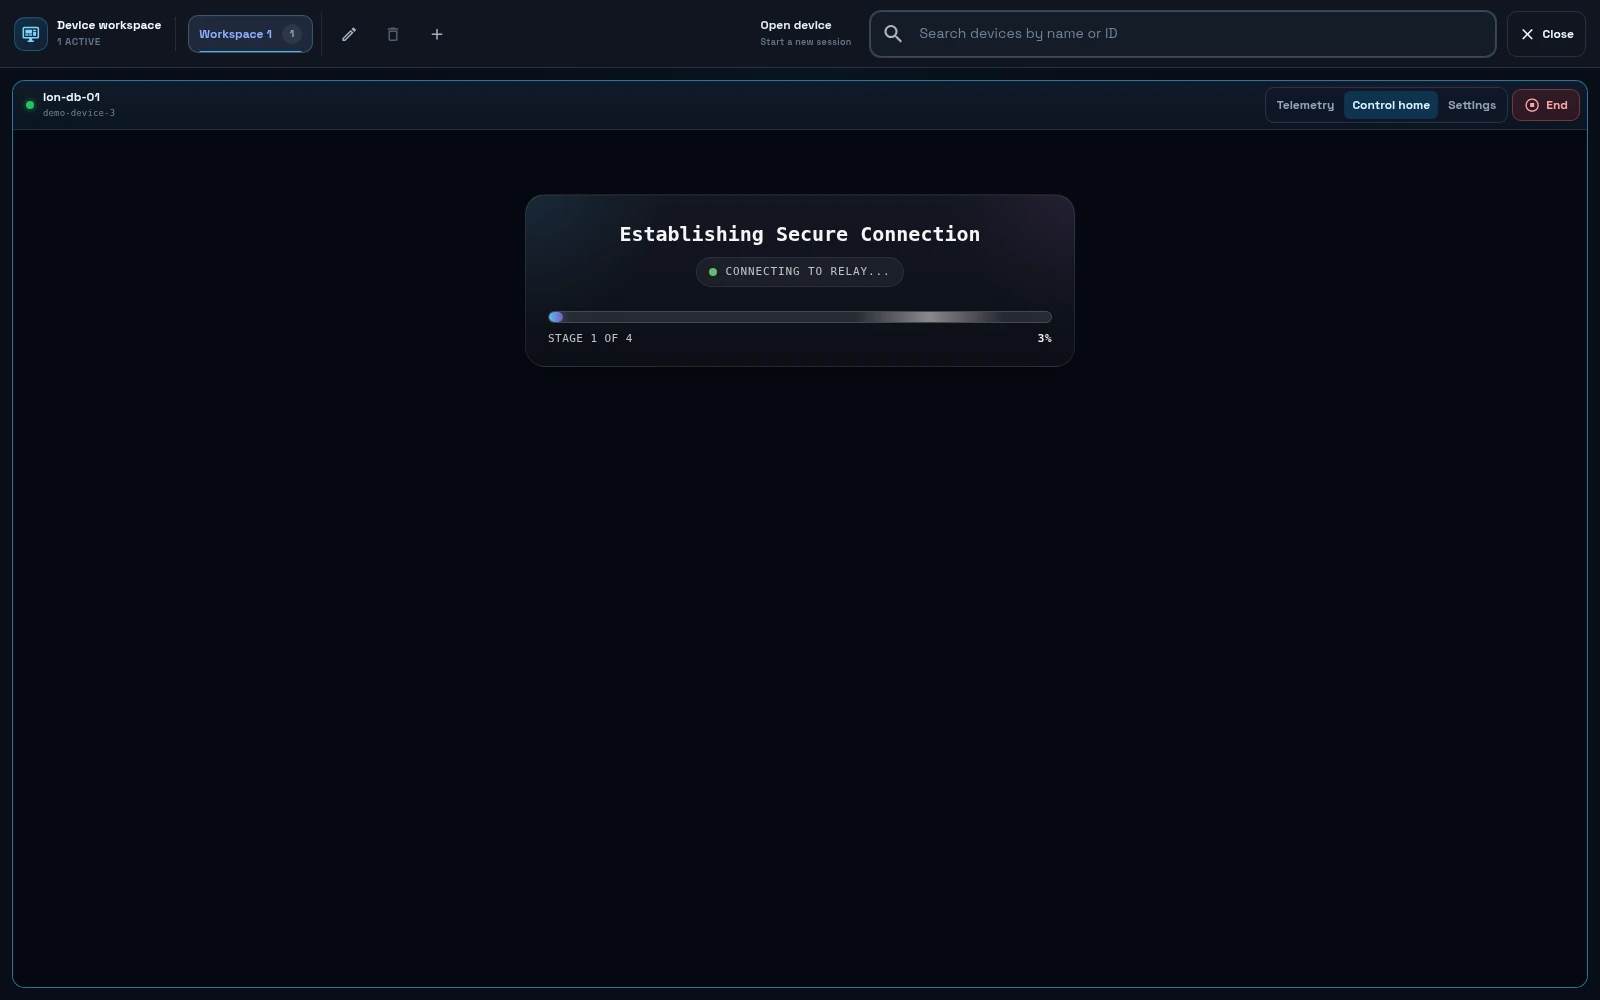
Connect securely
Open Control home to start the supported secure connection. The agent connects outbound; no public inbound management port is needed for this path.
Secure connection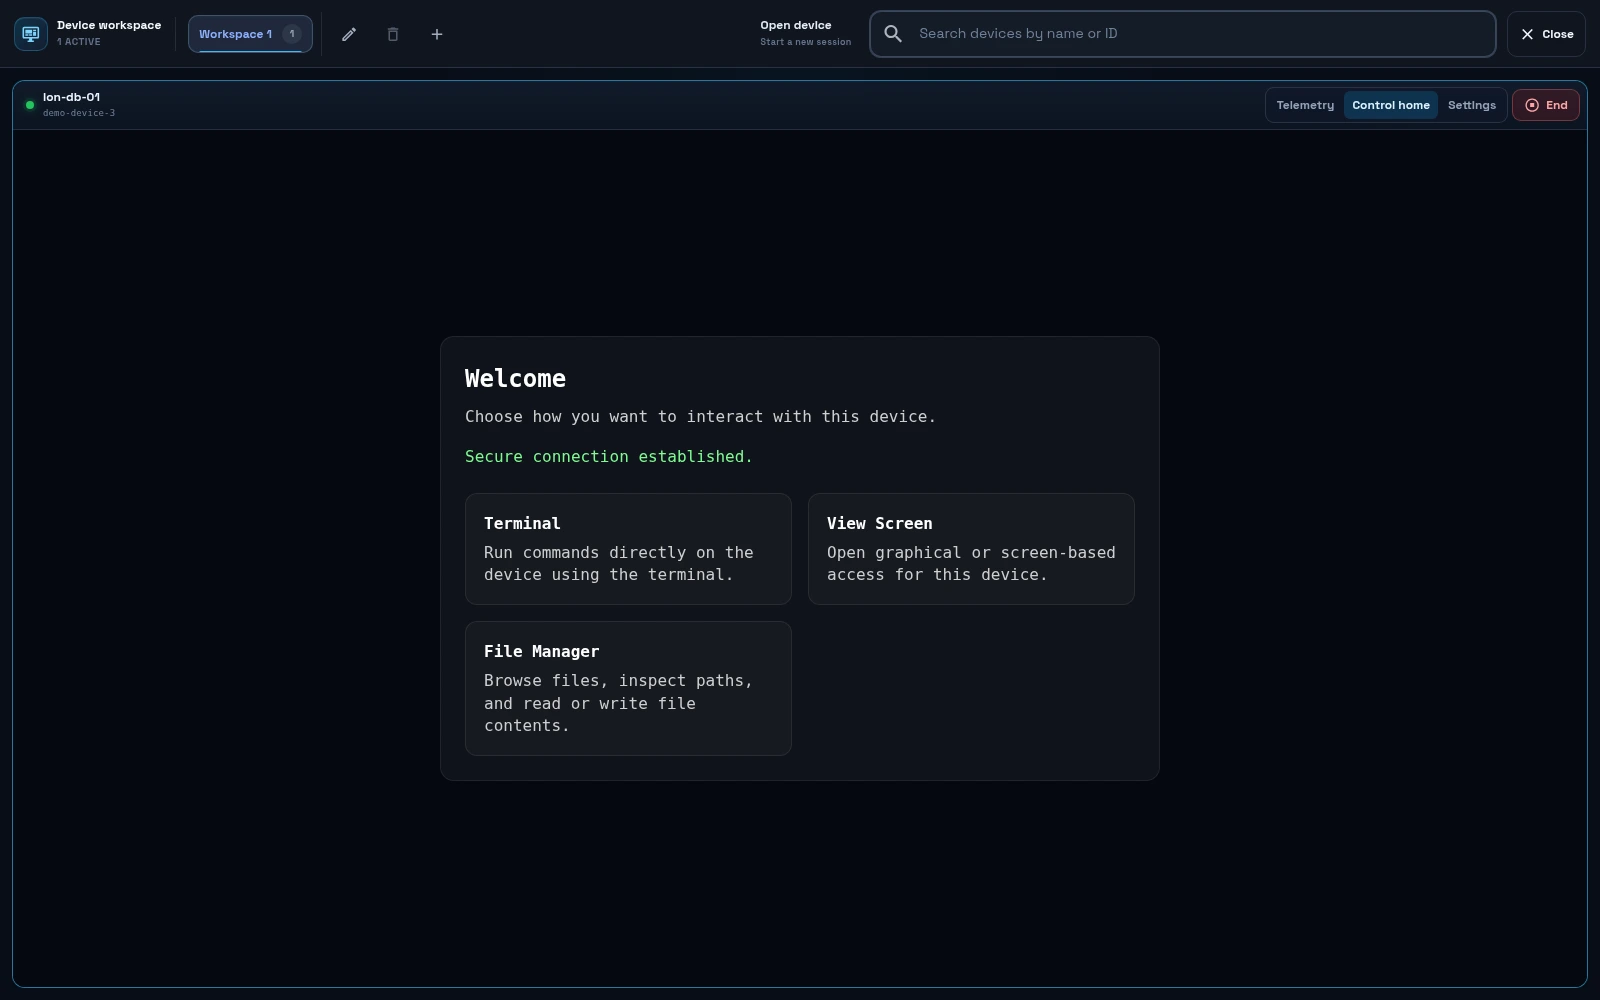
Choose your tool
Choose Terminal, View Screen or File Manager from the device workspace. Availability depends on the agent, platform and your permissions.
Device workspace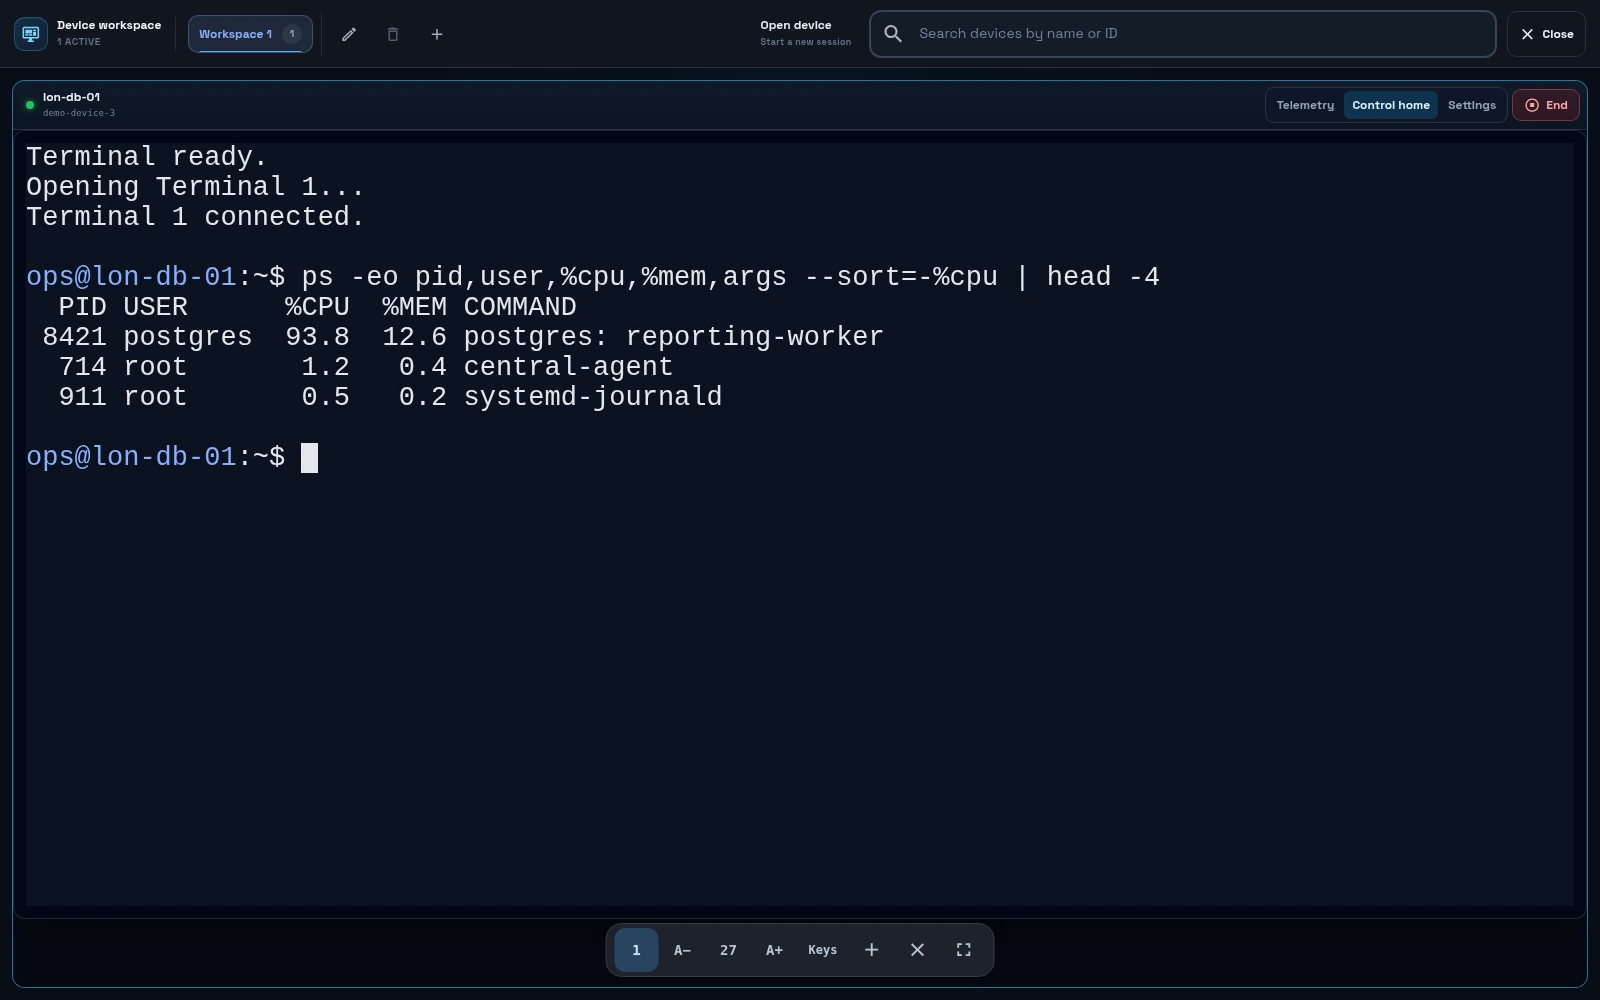
Investigate
Use the terminal to inspect running processes. In this example, a reporting worker accounts for the elevated CPU use.
Remote terminal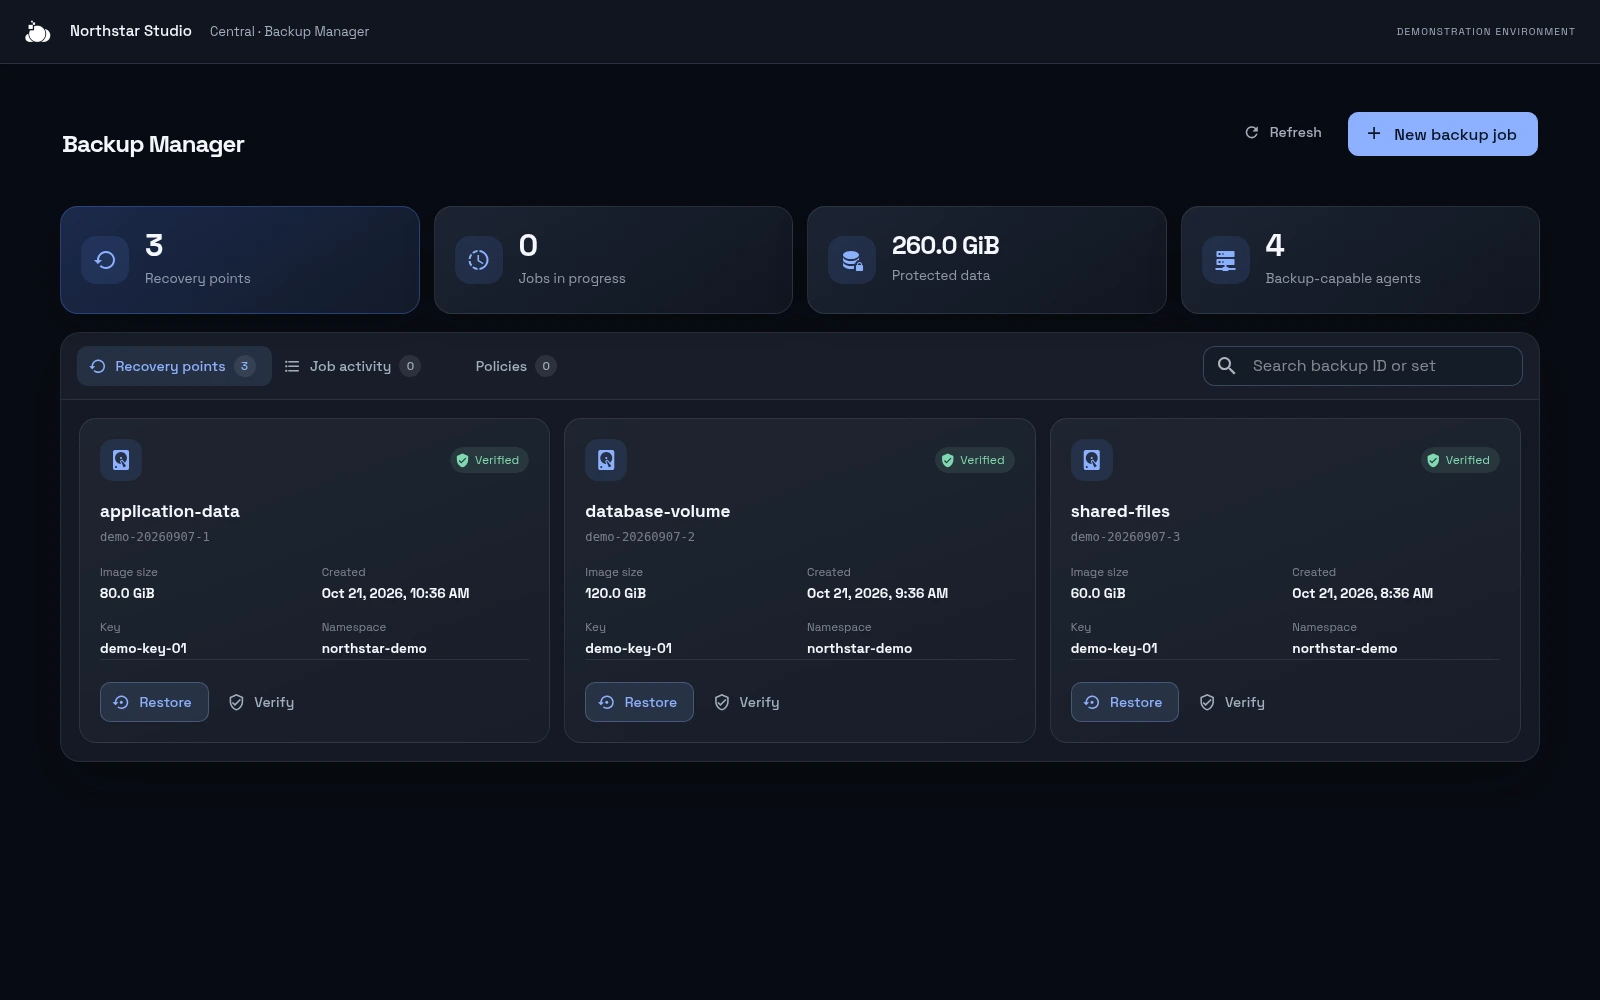
Review recovery
Review available recovery points and verification information in Backup Manager. Backup consumption is charged separately.
Backup ManagerActual Central components with fictional demonstration data. Connections and terminal output are simulated. Tools depend on your platform and permissions.
Find the affected server in your infrastructure view and review the health information or finding available for it.
Device monitoring ↗Select the device and open a supported terminal or remote desktop. Authorise protected access with your passkey when required.
Remote access ↗Supported management paths use the agent’s outbound connection. Investigate the service through the tools your role permits.
Connection modes ↗Check performance history and available recovery points. Backup consumption and managed recovery work are priced separately.
Backup and recovery ↗PRIVATE BY DESIGN
Keep management access controlled while working across the infrastructure you already run.
Supported agents connect outbound. You do not normally need public inbound SSH, RDP or other management ports for these paths.
Individual accounts and permissions govern access. Supported passkeys unlock the keychain used for protected owner-key operations.
Enrol compatible systems across existing hosting providers and sites. Central’s relay infrastructure supports the connection paths between them.
Connection modes have different encryption boundaries. Review service publishing and endpoint encryption ↗
LESS SWITCHING. MORE DOING.
Find a device. Understand its health. Open the tools you need. Central brings the everyday work of infrastructure management together.
Device health, inventory and performance history, organised around your infrastructure.
Monitor your systemsOpen supported remote desktop, terminal and service tools from the device you’re investigating.
Explore remote accessReach approved private services across sites without directly publishing their management ports.
Connect your infrastructureBuilt for compatible Windows and Linux agents. Tools depend on your platform and permissions. Check compatibility ↗
SECURITY, IN THE PRODUCT
See Central’s actual Secrets prompt, device workspace and maintenance approvals. Follow the choices that protect a new connection or a planned change.
Central / Open a deviceACTUAL UI · DEMO DATA
Protected access
When protected keys are locked, Control home brings up Central’s Secrets prompt. Signing in alone has not opened this new device connection.
Open a device
Verify identity
Choose Unlock Secrets. Central shows the verification step; your browser or authenticator handles the passkey check.
Open a device
Continue
After Secrets is unlocked, retry the connection if requested. This example reaches Terminal, View Screen and File Manager in the actual workspace.
Open a device Central / Approve maintenanceACTUAL UI · DEMO DATA
Review
Review the affected device and the maintenance request. Unlocking Secrets and approving this item are separate decisions.
Approve maintenance
Unlock
The original Secrets prompt explains why this infrastructure change needs saved credentials. Choose whether to continue.
Approve maintenance
Verify
Central waits for verification. This captures its own UI; browser and operating-system authentication prompts are not recreated.
Approve maintenance
Still pending
Secrets is now unlocked in this example, but the maintenance item is still waiting. You still need to review and approve it.
Approve maintenance
Choose a time
Select an earliest start time, review the affected host, then approve the update. The UI explains that services may restart.
Approve maintenance
Approval recorded
Central removes the approved item from the pending queue. The agent’s scheduled work and its outcome are separate from this approval record.
Approve maintenance Central / Cancel the unlockACTUAL UI · DEMO DATAYour choice
The actual prompt offers Cancel as well as Unlock Secrets. This is a new protected connection while Secrets is locked.
Cancel the unlock
Access stays closed
Cancelling leaves Secrets locked in this example. Central shows the unlock requirement rather than opening the device tools.
Cancel the unlockActual Central components with fictional devices and simulated verification, connections and approvals. No live device action is performed.
Signing in and unlocking Secrets are separate steps. For supported protected operations, a passkey helps unlock the keychain containing owner keys and saved credentials. A configured unlock session may cover more than one action.
WebAuthn verification belongs to your browser and authenticator. Biometric data is not sent to Central. This demonstration captures Central’s own UI; it does not recreate a browser or operating-system authentication prompt.
Maintenance and configuration changes still require the appropriate permissions and approval. An approval record is separate from an agent’s acknowledgement, execution and reported outcome.
START WITH WHAT YOU HAVE
Keep your servers, your hosting and your existing IT provider. Enrol supported devices into Central and bring your team’s work into one place.
See how the platform fits togetherSecure connectivity included in every plan.
POWERED BY CENTRAL. OPERATED BY DC CORE.
Run Central yourself, work with your IT provider, or ask DC Core to take on the operational work. Services are scoped around your people and systems.
Explore managed services ↗People, accounts, Microsoft 365 and supported PCs.
Monitoring, maintenance and agreed response for your systems.
Managed hosting from £42/month, excluding VAT, sized to your workload.
Capacity, retention and recovery operations matched to your requirements.
Managed services, cloud resources and backup consumption are quoted separately from the Central subscription.
CHECK THE DETAILS
Check compatibility, follow the enrolment steps and review public service telemetry before planning your deployment.
Review the enrolment process and the checks for your first supported device.
Read the setup guide ↗See current public control-plane and relay signals. These show present health; they are not an uptime history or a guarantee.
View platform status ↗Review access controls, connection boundaries and which team operates each part of your deployment.
Visit the Trust Centre ↗A FEW THINGS, UP FRONT
Understand what’s included, how access works and where to start.
Visit the Trust Centre ↗No. Keep your existing servers, hosting and IT provider. Install the Central agent on supported machines and enrol them into your organisation. See the first-device guide.
All Central software features and unlimited authorised users for compatible enrolled devices, plus standard monitoring, administration and interactive remote access. Backup consumption, cloud resources and managed services are separate. Compare packages and service boundaries.
Supported management paths use outbound agent connections, so you do not normally need a public inbound management port. Access depends on identity, permissions and the connection mode. Read the security and architecture details.
Yes. Send your work email and organisation through the Central form. We’ll confirm access and billing timing before activation and provide setup steps. Our team can assist with your first deployment. Start with Central.
GO A LITTLE DEEPER
Setup steps, private access and recovery planning.
Find a guide ↗COMPARE YOUR OPTIONSCompare Central with RMM, VPN and remote-access tools.
Explore comparisons ↗FREE PLANNING TOOLPlan your hosting and take the report to any provider.
Open the hosting planner ↗START SMALL. BUILD FROM HERE.
Central from £10/month for up to 5 devices, excluding VAT.
Your infrastructure. One place to manage it.